From a Forgotten S3 Token to Full AWS Root: Anatomy of a Real-World Cloud Takeover
A step-by-step forensic breakdown of an attack chain escalating an unprivileged S3 read token to full AWS organization root control via STS assume-role abuse.
IS
Isha SV
Cloud Security Consultant
Jul 15, 2026•7 min read
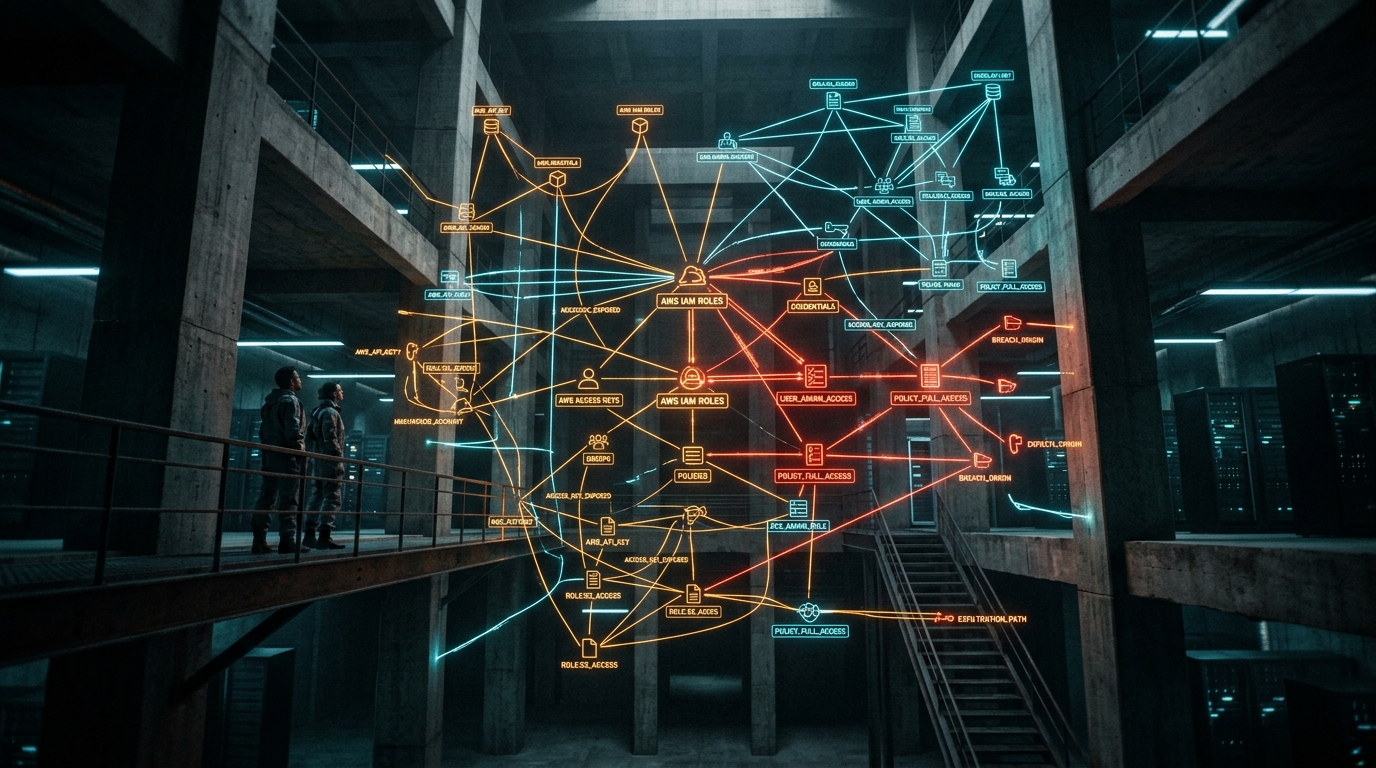
Anatomy of an AWS IAM Escalation: From Stale S3 Key to Root Control
During a recent simulated enterprise adversary engagement, our offensive security engineers gained initial footholds through a forgotten, read-only IAM access key embedded in an abandoned CI/CD pipeline.
Within four hours, this low-privilege read token was escalated into full organization-level root access across seventy AWS accounts. Here is the exact step-by-step forensic breakdown of how the privilege escalation occurred.
Cloud identity is the new enterprise perimeter. In complex multi-account environments, trust relationships between roles are frequently the most vulnerable lateral movement pathways.
The Multi-Step Escalation Chain
Critical Remediation Steps
Every organization running multi-account cloud estates should implement the following guardrails:
IS
Published by
Isha SV
Cloud Security Consultant